What a program office, a contracts officer or an assessor tends to ask. Questions we cannot yet answer with verified facts are left off.
Yes. Delivery happens inside the FedRAMP-authorized GovCloud boundary, with US-based personnel and a cleared principal. If your program requires commercial Salesforce instead, we'll say so.
We're boutique on purpose. A single-program subcontractor with fifteen seats is a good fit; so is an ISV that needs senior Apex capacity for two quarters. If we're the wrong partner, we'll tell you in the first call.
You'll work with the principal who scoped your engagement, backed by a small vetted US bench for surge capacity. No handoff to an offshore delivery team after the sale.
No offshore delivery. Surge capacity comes from a small vetted US-based bench, and anyone touching your org is named to you in advance.
Everything lives in your environment: metadata in your repository, decisions written down, and a handover document maintained during the engagement rather than at the end. You could hand the work to another partner without archaeology.
Yes. Plenty of defense suppliers run commercial Salesforce entirely legitimately because the data in scope isn't controlled. We'll tell you which one your requirement actually calls for rather than upselling the harder environment.
Common, and not a problem. We're often brought in for the GovCloud or compliance-sensitive slice alongside an existing partner, or for a second opinion on an architecture before it's built.
Our principal holds Registered Practitioner Advanced (RPA) status from the Cyber AB, the accreditation body for CMMC. That is the ecosystem's credential for implementers who help organizations prepare, and it binds us to the CMMC Code of Professional Conduct. It is not an assessment authority, and it is not a statement that your org is certified , only a C3PAO can do that. The firm itself is separately registered as a Registered Practitioner Organization (RPO), which is the organization-level registration for non-certified CMMC consulting. Ask us for both registration details and we'll send them.
We build and evidence the platform side, data model, sharing, logging, CUI handling, and work alongside your C3PAO or consultant. We don't certify our own work.
Two different things, and we keep them separate. Every managed services engagement includes an Org Security Review: a read-only review of your Salesforce configuration, permissions, guest and external surface, custom code and connected apps, with findings mapped to NIST SP 800-171 controls and an hour estimate against each fix. That is evidence you can hand an assessor. It is not a penetration test, and we do not call it one. A true penetration test is a separate, one-time engagement, priced on its own, we scope and manage it, and it is performed either by our team or by a specialist US-based testing firm we select and manage, depending on the scope. We stay responsible for translating the findings into remediation and re-testing the fixes. Worth knowing before you buy one: CMMC Level 1 and Level 2 do not require a penetration test. Only Level 3 does. If someone tells you otherwise, ask them which control.
Controlled data stays inside the authorized boundary. It isn't copied to laptops, sandboxes, ticket attachments or AI tooling; where a task needs realistic data we use masked test data. If your program has specific handling instructions, send them and we'll work to them.
Yes, from the unclassified side. We build and test releases in an IL5 or unclassified mirror of your org, then hand your cleared staff packages, a manifest and a deployment runbook for the air‑gapped org. We don't hold a facility clearance; for classified access we work through a cleared prime.
Access is scoped to the statement of work, documented, and removed at close-out. If you'd rather provision a named user under your own controls than issue a partner credential, that's fine , often preferred.
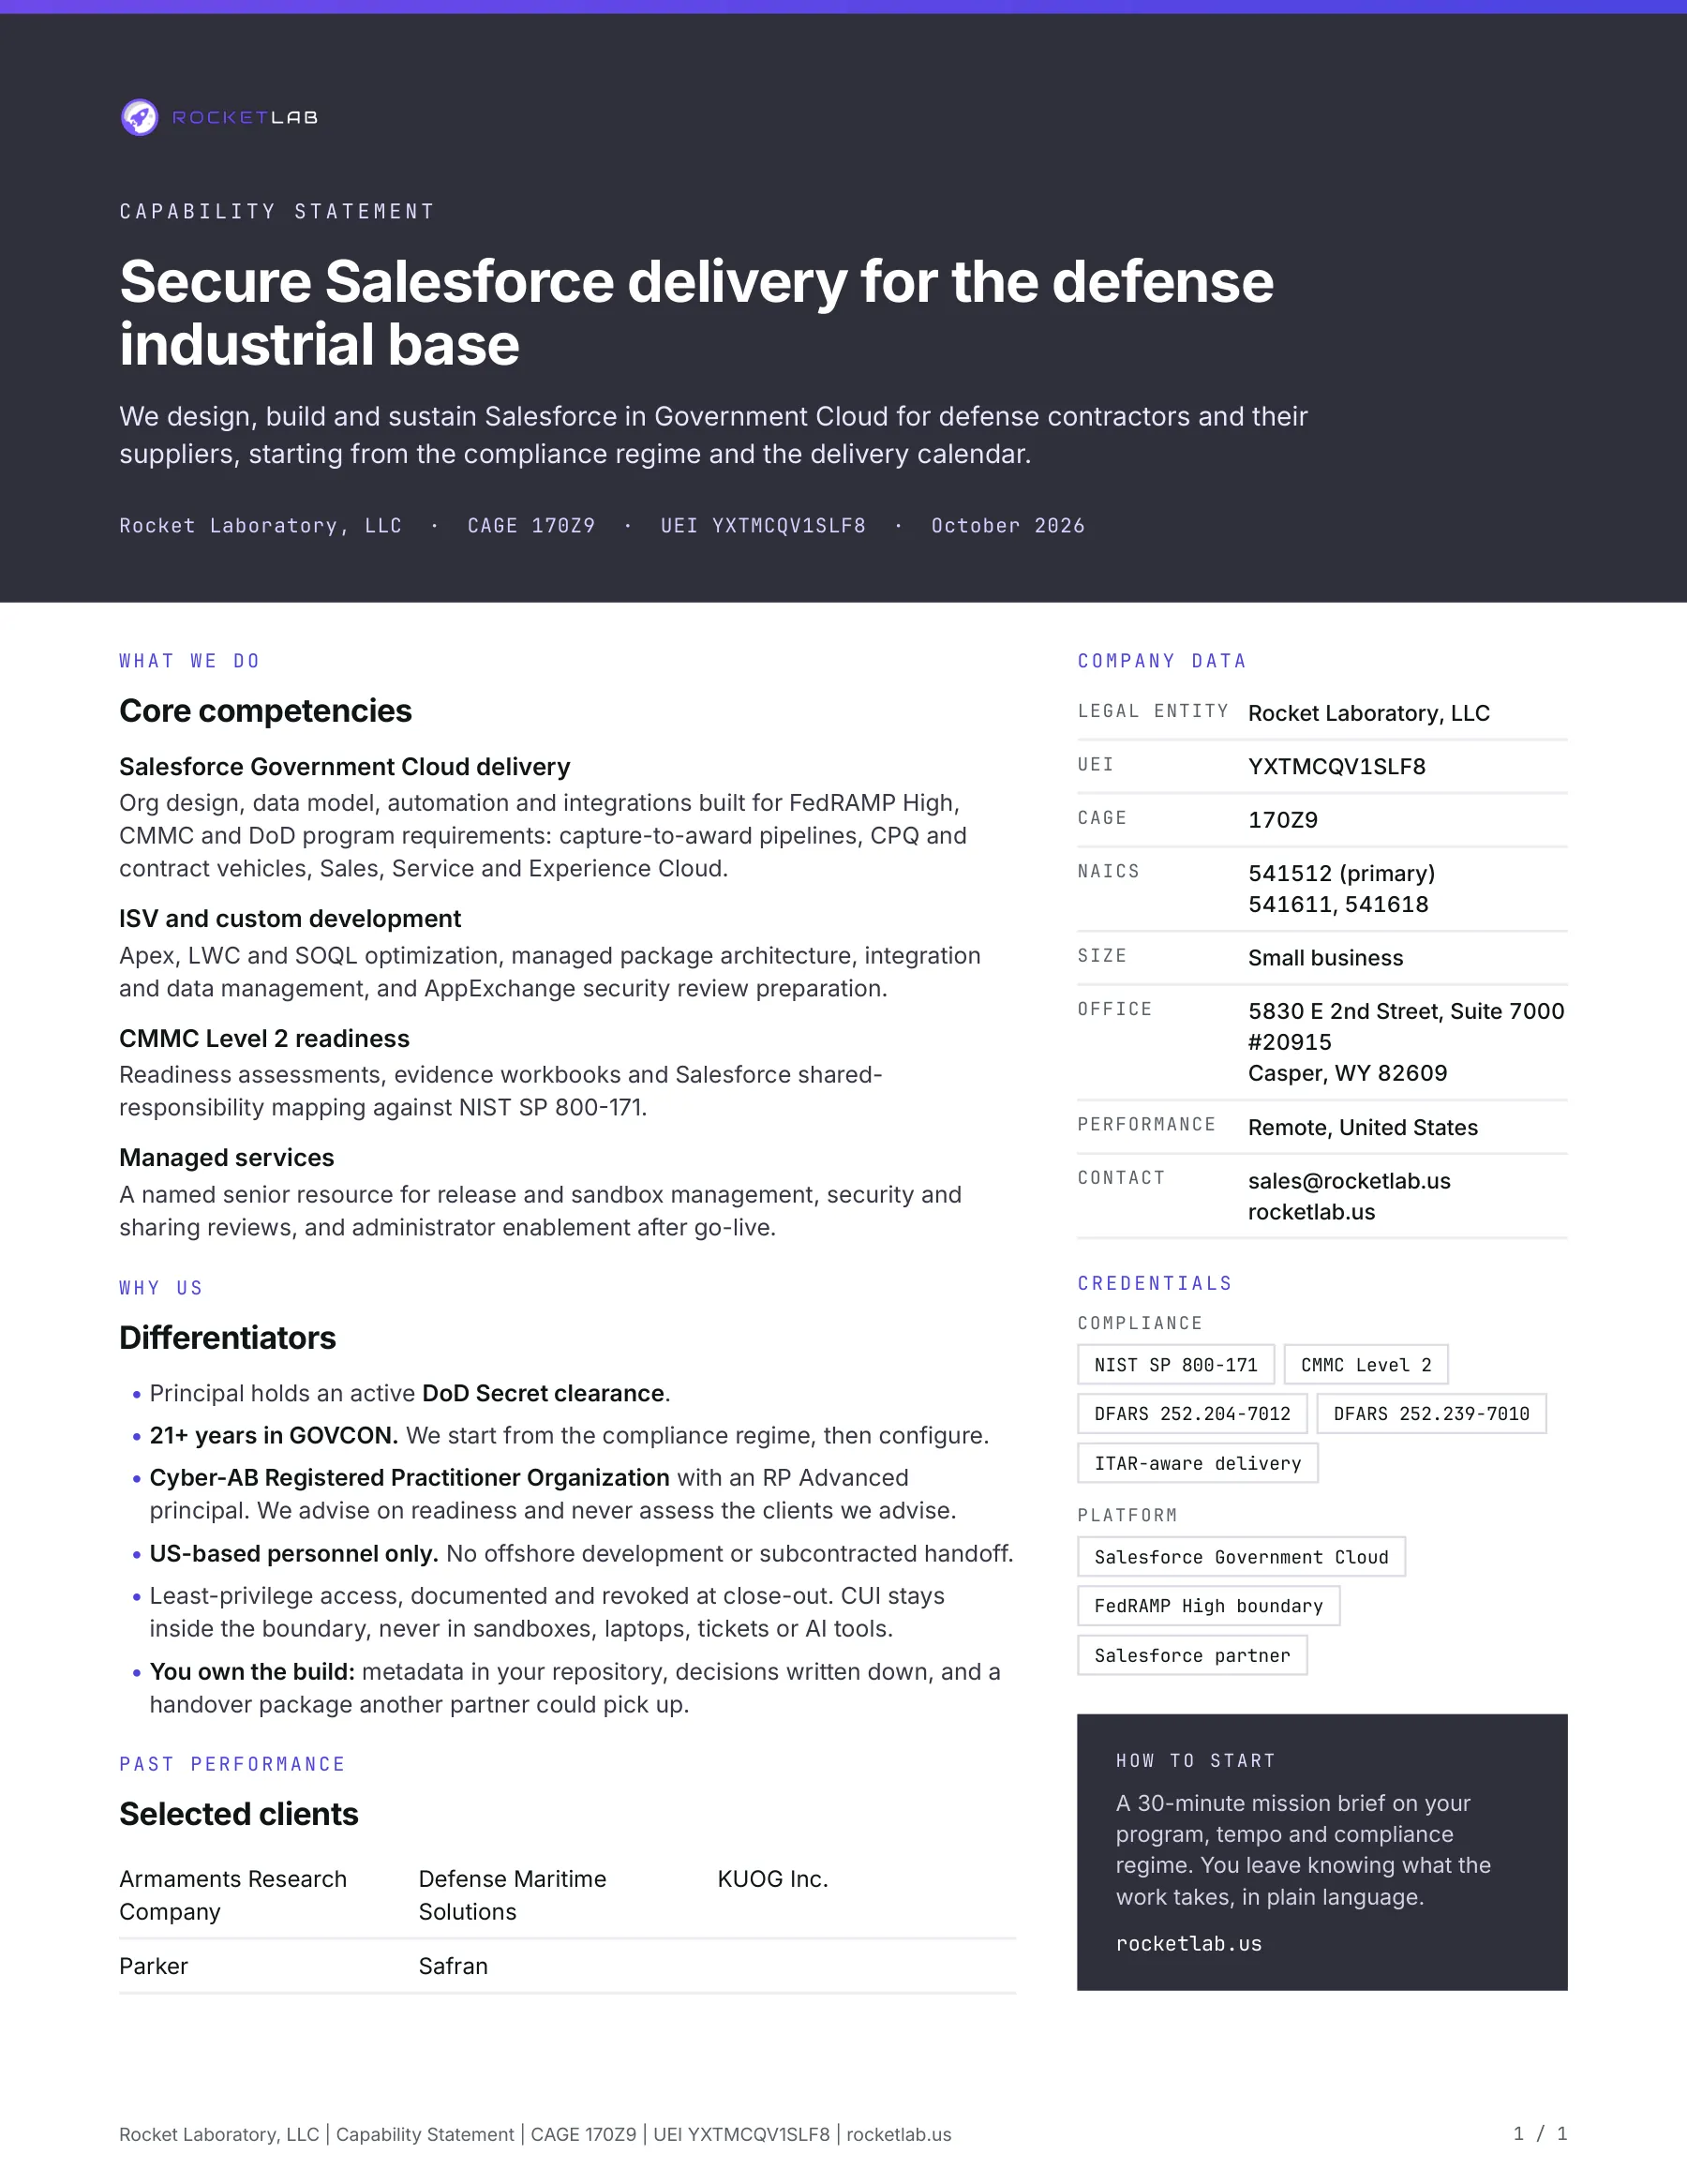
Yes , Rocket Laboratory, LLC, CAGE 170Z9, UEI YXTMCQV1SLF8, registered in SAM.gov. Happy to send a capability statement with the current registration expiry on request.
Both. On platform work we're comfortable as prime; on larger program efforts we're usually the Salesforce piece under a systems integrator or a program prime, which is often the faster path to get us on contract.
Rocket Laboratory, LLC is a small business under NAICS 541512, with no socio-economic set-aside designations. If your requirement depends on a specific designation, say so early , we will tell you plainly whether we qualify rather than let it surface at award.
Yes. We work to written acceptance criteria and a documented schedule so performance is measurable rather than argued about after the fact. Past-performance references available on request, with client permission.
Yes, and we read them. Flow-down clauses on cybersecurity, CUI handling and place of performance are ones we've worked under before, so review is usually quick.
Ask it on a mission brief, or send it to sales@rocketlab.us and get a straight answer in writing.
One percent of Rocket Lab revenue is committed to permanent carbon removal, not offsets, and not renewable-energy credits against emissions already released.
Stripe aggregates contributions from member businesses and buys removal through Frontier, its in-house team of science and commercial experts, as an advance market commitment. Pooling demand is the point: no single small firm can move a technology down the cost curve, but 25,000 of them can.
These are two examples from a broader portfolio of early-stage removal technologies, selected by Stripe's scientific reviewers. Rocket Lab chooses the commitment, not the projects.